
Single Sign-On
Your own Directory
Simplify user self-enrollment with our OAuth, SAML v2 integrations for identity federation.
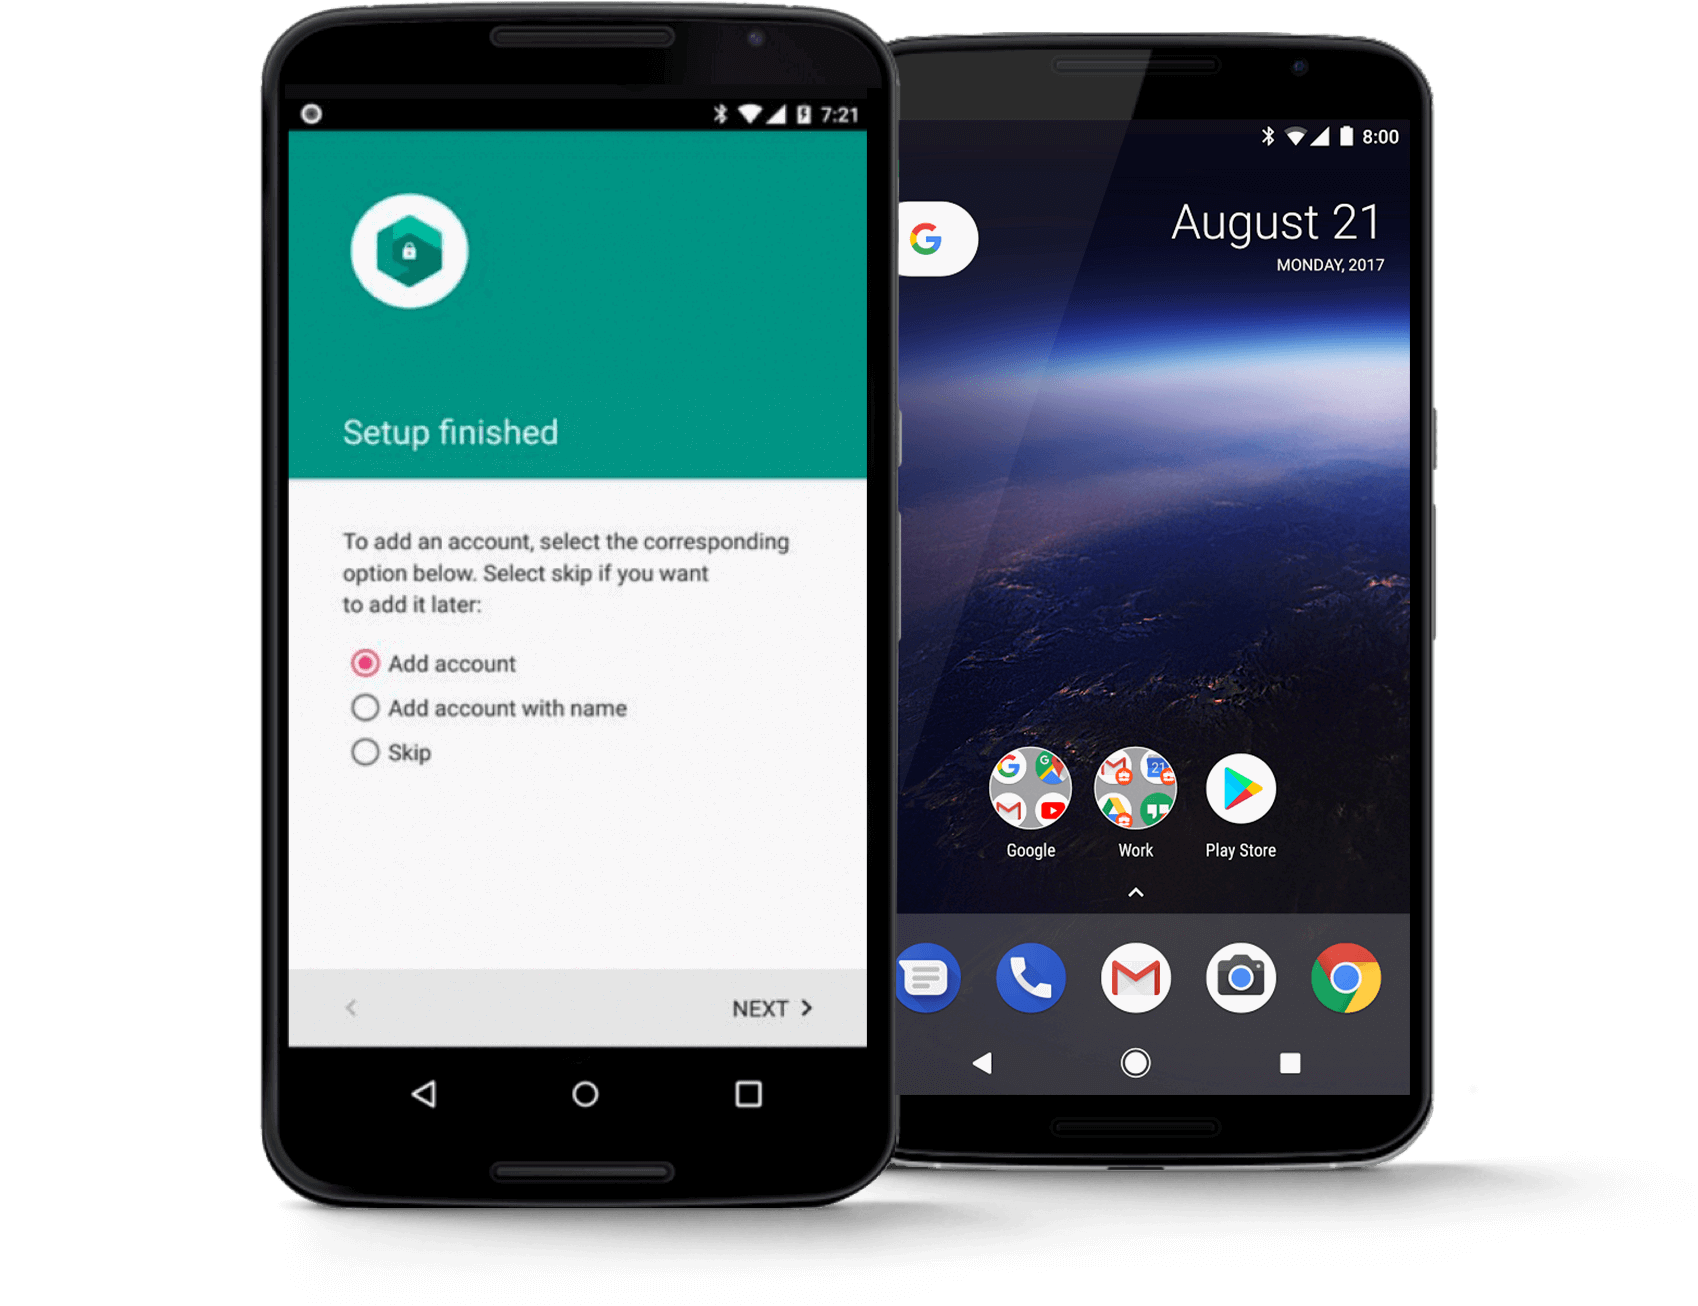
Set up the work profile on Android personal devices to separate your employees' work apps and data from personal apps and data.
With a work profile, users can securely and privately use the same device for work and personal purposes, your organization manages your work apps and data while your personal apps, data, and usage remain private.
Employees can work on their personal phones without sharing anything personal. Between work and personal profiles, every app stays separate, emails, calendars, docs, photos. The two versions never share data. The IT team just uses Mobile Application Management and never touch anything personal.
Employees can use your company credentials and handle the process by themselves from start to finish.
Apps can be targeted by user groups and be defined as mandatory. Appaloosa supports public mobile apps as well as private and web mobile apps.
Appaloosa creates a secure container for your work data and separate the private applications from the work applications. Administrators can then remotely manage the work container and deploy applications silently to any device running. Users remain in full control of their personal data.
Manage how your corporate apps are accessed: restricted sharing and app installs, screen lock policy and VPN.
In the event of a lost, stolen device or employee termination, IT can remotely wipe corporate data from the employee device.
Highlights
Explore our blog to learn about Android Device Management, Android Enterprise & Work Profile.